

ContribKanban now tracks GitLab work items
WordPal Converts WordPress Block Themes for Drupal Canvas and Display Builder
Vale 1.0.0; prose linting for Drupal
Drupal is 25 this year, and its code has had linters for a long time. Its words haven't, and with Drupal AI writing straight into the node form, more of them now come from a model. A search of drupal.org turns up readability scores and spellcheckers, but nothing that holds a save to your own style guide.
Vale (for Drupal) does that with the Vale prose linter. Break an error-level rule and the save is refused, or only the publish if drafts should save freely. 1.0.0 is out now for Drupal 10.3, 11 and 12, and needs the Vale binary on your server.
Vale in CI is the right tool for Markdown in a repository. Content in Drupal arrives through a save instead: the node form, a Fully Decoupled frontend over JSON:API, a workspace being published. The module checks there, on the server, whatever editor the author used.
In the Open with Tiffany Farriss: What it takes to sustain the Drupal commons
In the Open is a weekly series from Drupal Association Interim CEO Tiffany Farriss, sharing what she is hearing across the Drupal community and where the Association is headed. In this episode: why Drupal's commons is under pressure, how the Drupal Certified Partner program is evolving, and what it takes to keep free software running for the next 25 years.
"Drupal is free. The code of Drupal is free forever. But those of us who run Drupal know that running Drupal has never been free."
The following is a transcript of Tiffany's remarks, lightly edited for readability.
What I'm hearing from the communityThe thing that's top of mind for me this week is reflection. I've spent a lot of time listening to folks, talking to folks, asking a lot of questions. I wanted to take a few minutes to share back some of the things I'm hearing, because these are the things motivating the changes in how I'm thinking about existing programs, and about how we might want to do things differently for the next 25 years of Drupal.
Whether it was the ecosystem survey, the business community survey, or conversations with the core release maintainers and other parts of the community, it's very clear to me that our commons is fragile. The technology of Drupal itself is a brick. It is solid. We are super proud of our security team. But the people and the funding sustaining it aren't yet in a sustainable place, and there's a lot of pressure.
That pressure is echoed in the business community. The businesses that have been very supportive of Drupal through the years, and I'm thinking not just of those 126 Drupal Certified Partners but of all of us, everyone is getting squeezed. The business survey data showed that the average deal size was down, and that pipeline expectations had gone negative for the first time in the Drupal business survey.
From Malloc to Match (Part 1): The Evolution of PHP Through the Lens of a Systems Programmer
This is Part 1 of a two-part series about the trades PHP made early on and what they have meant for Drupal performance. Part 2 covers the Java-fication of Drupal, the engine-level work that saved PHP from itself, and how Drupal came full circle, with its biggest performance gains in a decade.
Supply Chain Security for Drupal Projects
A developer needs a fix from a contrib module, so they open a terminal inside DDEV and run composer update. The container can reach an SSH agent and a hosting token. Composer downloads a few packages and writes a new lock file.
Nothing about that looks unusual. That is the problem.
The recent wave of supply chain attacks did not exploit Drupal. It exploited the moment a developer or a build changes dependencies with credentials in reach. The Drupal Security Team has been clear about the boundary. Its remit is code hosted on Drupal.org, and site owners are responsible for third-party libraries.
The rest of the dependency tree is ours.
We develop locally in DDEV and use Dependabot in GitHub for update pull requests. Here is how we think about protecting a Composer-based Drupal project.
The risk arrives when dependencies changeThese attacks arrive with a dependency change, and a Drupal project gives them three places to run.
The first is Composer plugins. In April 2026, an attacker moved an existing intercom/intercom-php tag to a malicious commit. The malicious commit turned the library into a Composer plugin that stole credentials during install.
Your First Drupal AI Workflow: Draft Replies to Website Inquiries

Turn Drupal website inquiries into proposed email replies your team can review. This guide explains how Webform, ECA, and Drupal’s AI framework work together, with practical setup steps and checks before launch.
Webinar: Can AI help your website guide people to their next step? Join us October 29, 2026
Your website may have the information people need. But the way they discover and evaluate their options is changing, with AI-generated answers becoming part of the journey.
EAB’s survey of more than 5,000 U.S. high school students, conducted in late 2025 and published in February 2026, 46% reported using AI tools during their college search, up from 26% in spring 2025. A separate EAB survey published in August 2026 found that 57% of more than 2,500 U.S. parents surveyed had used AI to evaluate colleges and compare options for their children.
Together, these findings suggest that students and families are adding conversational tools to the ways they research universities. For institutions, that raises a practical question: could a more guided experience also help people make sense of the information on their own websites?
Growing adoption doesn’t mean trust is guaranteed. Pew Research Center found that 66% of U.S. adults were extremely or very concerned about people getting inaccurate information from AI. For institutions exploring AI-assisted guidance, that makes accuracy, transparency, and testing with real users central to the experience.
For Higher Education institutions, this raises a practical question: could a more guided experience help students and families make sense of institutional information while preserving accuracy, trust, and control?
Vibing Drupal: Using AI to switch between multiple versions of Drupal core
With Drupal 12 on the horizon and Drupal 10 reaching end of life in December, I'm facing two challenges. First, I need to upgrade my current site from Drupal 10 to Drupal 11. Second, I need to update my contributed modules to support Drupal 12, while still supporting Drupal 10. Frankly, I am more anxious about upgrading to Drupal 11 and supporting Drupal 12 than about integrating AI into my workflow.
Upgrading to Drupal 11
Upgrading to Drupal 11 has gotten easier over the years thanks to tools such as Drupal Rector, the Drupal Lenient Composer Plugin, the Upgrade Status module, and the Project Update Bot. Still, if you rely on contrib and custom modules, you'll have a lot to tweak and test.
I've done a "big-bang" upgrade via a dedicated branch, using the Lenient plugin and the Project Update Bot's patches for contrib modules, and fixing deprecations in custom code with Drupal Rector. There were always a few rough edges. Ideally, I'd like to gradually test my upgrade to Drupal 11 while continuing to support Drupal 10 in the same codebase using the DeprecationHelper.
As a maintainer of a contributed module, I face a slightly different challenge: supporting Drupal 12, 11, and 10.
Supporting Drupal 10, 11, and 12
Can Governments Reduce Microsoft 365 Dependency Without Replacing It?
Our DrupalCon Rotterdam 2026 recap: concurrency, multilingual and page builders
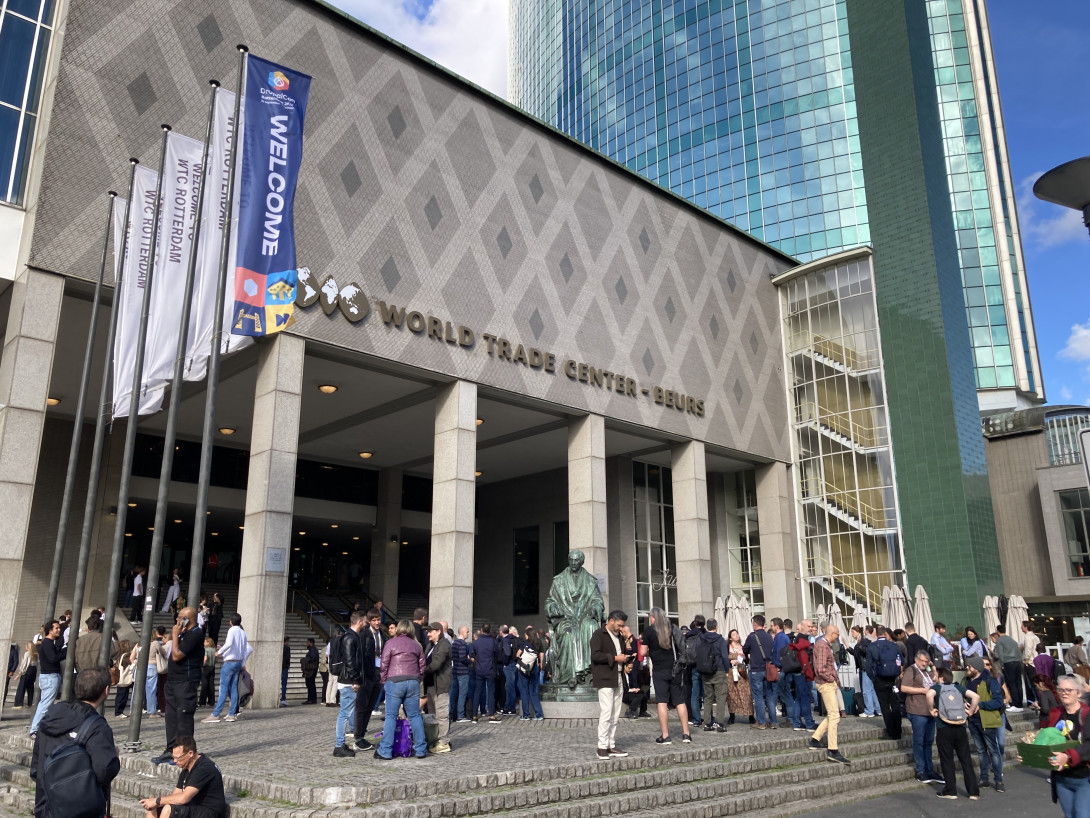
We are back from Rotterdam, and we are still blown away. Three weeks later we are still processing what happened. We brought a whole bouquet of topics: structured concurrency for PHP, Translation Bliss, our page builder session and CrowdPower.Digital. Some days felt a bit like a movie. One conversation led to the next, and suddenly we were at a table with people whose names we have read in the issue queue for years.
Outer-Core Beta Revives Drupal Space Game, With New Universe Planned
DDEV October 2026: PHP2Shell Fixed in v1.25.5, Thanks to Ondřej Surý and the PHP Foundation
 PHP2Shell, and DDEV v1.25.5
On October 21, PHP released 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to fix CVE-2026-109618 and CVE-2026-109619, nicknamed "PHP2Shell". A single unauthenticated request could run code on any server running PHP. PHP's security advisory↗ has the details.
Local DDEV projects listen only on your own computer, so nobody on the internet could reach them. Projects exposed with ddev share or used for casual hosting↗ were at risk, and so were your production servers. Stas wrote up the same day what DDEV users needed to do, including how to get the fixed PHP into projects before a new DDEV release: PHP2Shell: What DDEV Users Need to Know.
DDEV v1.25.5 shipped on October 26 with the fixed PHP in ddev-webserver. PHP 8.1 and older are past end of life and get no fixes from PHP, but deb.sury.org patched every version it ships, so PHP 5.6 through 8.1 in DDEV are fixed too. Upgrade, run ddev restart, and check ddev php -v. If you haven't updated PHP on the servers where your sites are hosted, do that first.
v1.25.5 also brings 142 community PRs that were waiting for the next release:
Improve User Experience By Creating a Fast Sign-Up & Login Flow in Drupal
The authentication screen can have a significant impact on both first impressions and user retention. Manual credential management can create friction that actively drives users away. That being said, simplifying authentication is one of the ways UX design can increase conversions on your Drupal website.
Should We Adapt to AI, or Should AI Adapt to Us? Aidan's Foster's Perspective
Akismet turns 21. Spam isn’t invited.
On October 25, Akismet turns 21. We’re celebrating with a few new guests: an official Drupal module, a PHP SDK, and another year of improvements to our WordPress plugin. Spam still isn’t on the list.
Akismet launched in October 2005 to help people spend less time dealing with comment spam and more time enjoying their blogs. The web has changed a lot since then. People build communities, collect inquiries, accept donations, and create applications on all kinds of platforms. Each of those places gives people a way to contribute. It also gives spammers somewhere to try their luck.
Since then, Akismet has blocked over 570 billion pieces of spam. Every one is something a site owner didn’t have to spend time sorting through. Our birthday wish is to keep making more room for the real people.
Welcome, Drupal
This year, we released the official Akismet Drupal module, built by the team behind Akismet. It brings our spam protection to Drupal comments, contact forms, webforms, and user registrations, with tools for moderators to review submissions and send corrections back to Akismet.
We’ve continued building on that welcome. The latest release supports Drupal 12 and passes richer bot-detection signals into spam scoring. On Drupal 12, comments and registrations are supported now; contact forms, webforms, and the Key module will follow as those modules become ready for Drupal 12.
If Knowledge Belongs to Everyone, Why Does It Cost So Much?
Opening access is only the first step. Sustaining the people, institutions and infrastructure that keep knowledge available is the greater challenge.
Behind every published research paper lies years of work, often supported by public funding. Yet the institutions producing that knowledge do not necessarily control how it reaches the world. New research released by SPARC on 14 October, ahead of International Open Access Week, estimates that more than 95% of investment in a typical research article occurs before publisher submission, based on its accounting model. A companion study found operating margins of 24% to 38% among major academic publishers in 2025. The figures raise an uncomfortable question: who should benefit from knowledge that society has largely paid to create?
Removing paywalls is important, but it does not automatically make scholarly publishing fair or sustainable. Some open-access models shift costs from readers to researchers through publication fees, potentially excluding scholars with fewer resources. Alternatives exist. Harvard Library, for instance, supports journals that charge neither authors nor readers. Such models still require institutional investment, editorial labour and dependable technology. The real challenge is not simply making research available, but ensuring that openness does not depend on another form of exclusion.
What Drupal's AI Contribution Policy Requires from Contributors
3 Tips for Incorporating Colour Psychology in Website Design
How we patched 30+ enterprise client sites for a Critical PHP Vulnerability within 24 Hours (and what we found when we looked back)
Pages
